SBI Confirms Notification to Customers After Data Breach
State Bank of India assures affected customers of data safety following a recent breach.
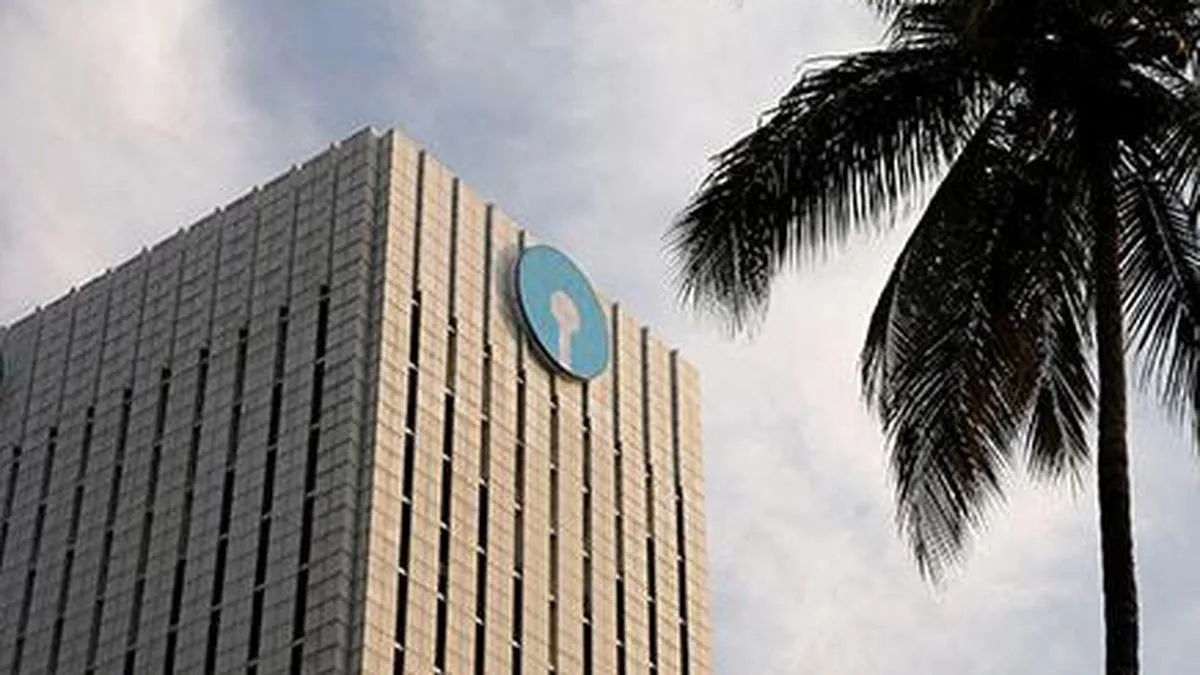
SBI has informed all affected customers via email and WhatsApp.
3,897 records containing personal information were found on the dark web.
Customers are urged to practice safe digital banking.
In response to a recent data breach, the State Bank of India (SBI) announced on October 23, 2026, that it has individually notified all customers whose data was compromised. Notifications were sent through email and WhatsApp, ensuring that those affected are aware of the situation.
The bank reassured its customers, stating, "We reiterate that your account balances and funds are safe with us." SBI emphasized the importance of safe digital banking practices, advising customers to never share their OTP, PIN, or passwords, and to remain cautious of suspicious communications.
This incident has drawn criticism towards SBI for its initial failure to inform affected customers directly, despite notifying stock exchanges about the breach. Earlier in October, SBI received alerts from its Threat Intelligence Service Provider, the Defence Cyber Agency, and CERT-In regarding the potential exposure of customer data on the dark web. The bank officially reported the incident to stock exchanges on October 21, 2026.
According to SBI, a preliminary analysis revealed that out of approximately 375,000 records available on the dark web, 3,897 contained Personally Identifiable Information (PII). This exposed data included sensitive customer details such as mobile numbers, dates of birth, names, gender, email addresses, residential addresses, and identifiers related to loans and branches.
SBI stated that a comprehensive investigation is underway to verify the authenticity of the exposed data, identify the source of the breach, and evaluate the potential risks to both customers and the bank. The bank is committed to ensuring the safety and security of its customers' information moving forward.