Satya Nadella Warns of Unpatchable Vulnerabilities in Critical Infrastructure
At the DealBook Summit, Microsoft CEO highlights the risks of AI-driven cyberattacks on America's software systems.
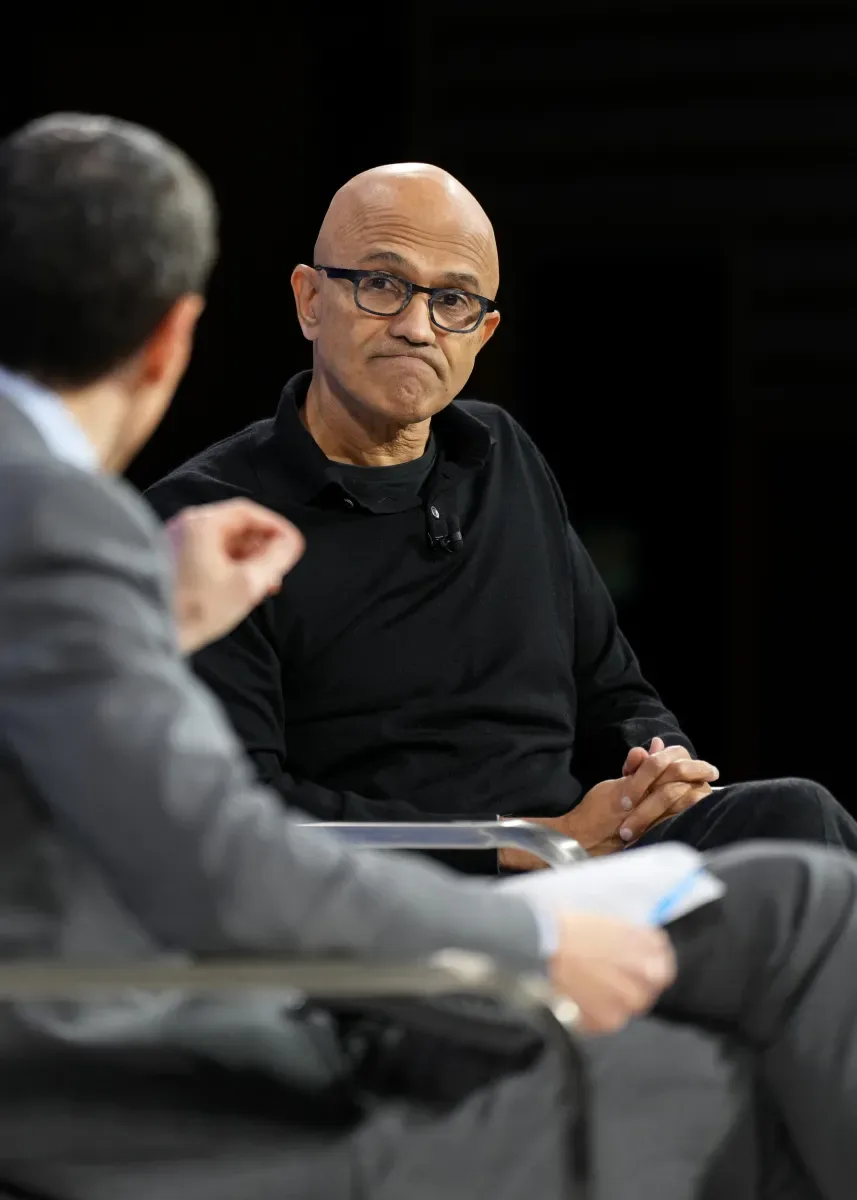
Satya Nadella emphasizes many critical systems are unpatchable.
Recent outages raise concerns about potential cyberattacks.
AI has accelerated the need for rapid software patching.
During a recent discussion at The New York Times’ DealBook Summit, Microsoft CEO Satya Nadella expressed serious concerns regarding vulnerabilities in America's critical software infrastructure. He pointed out that numerous systems, including those that manage essential hardware and transportation networks, contain flaws that cannot be fixed. Nadella stated, "Remember, there is a lot of stuff in our critical infrastructure that’s unpatchable," highlighting the risks posed by AI-enhanced cyber threats.
Nadella's remarks come in the wake of significant outages affecting major services, including Microsoft Outlook, the NSA, and Apple. Although officials have denied that these disruptions were due to cyberattacks, the frequency of such incidents has sparked fears about the security of vital systems. Nadella noted that the increasing interconnectivity of previously isolated devices has created new vulnerabilities that are ripe for exploitation.
In discussing the recent Outlook outage, Nadella described it as a result of a "latent bug" that culminated in a "perfect storm" of issues. He assured that Microsoft is taking steps to learn from this incident, stating, "We put out an incident response, and we’re going to obviously take all of the learnings, both upstream architectural, as well as operational, and fix that."
The conversation also touched on the broader implications of unpatchable firmware in transportation systems. Nadella emphasized the necessity for modernization and the importance of assessing threat vectors to enhance detection and defense capabilities. He acknowledged that while tools to identify vulnerabilities have improved, the rapid pace of potential exploitation has made it increasingly challenging for companies to manage these risks effectively.
Nadella concluded by addressing the urgency of patching vulnerabilities, noting that the speed at which patches must be deployed has increased significantly. He remarked, "The patch [now] needs to go instantly from being available to being patched in production, because it’s being exploited in the wild, right? So that’s going to create instability." This highlights the pressing need for organizations to adapt to the evolving landscape of cybersecurity threats.