eMudhra Exits Global SSL/TLS Market Following Key Compromise
eMudhra's decision to withdraw from the global SSL/TLS certificate business comes after vulnerabilities in its intermediate CA keys were discovered.
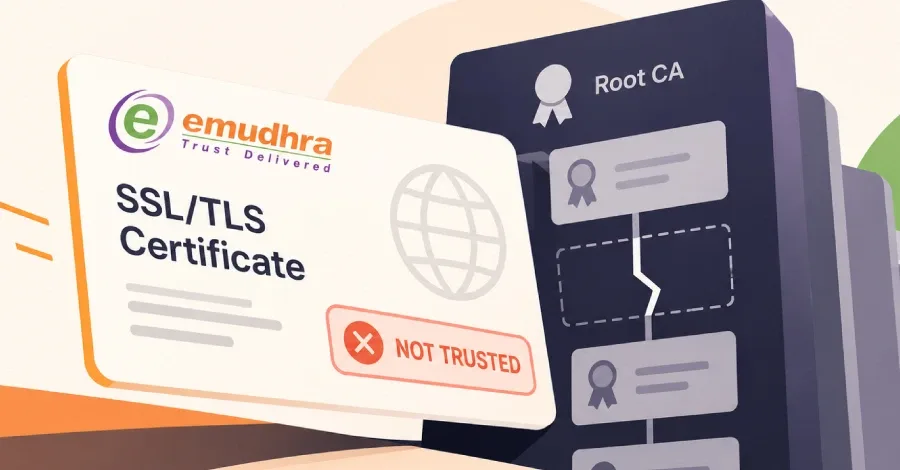
eMudhra will exit the global SSL/TLS certificate market after eight intermediate CA keys were found to be easily guessable.
The company plans to replace affected certificates with free alternatives, although specific partners have not been disclosed.
Chrome and Firefox will stop trusting eMudhra's root certificate, impacting approximately 30,800 certificates.
eMudhra, an Indian certificate authority, has announced its withdrawal from the global SSL/TLS certificate business, a decision made by its board on Thursday. This move follows the revelation that eight of its intermediate CA certificates had easily guessable private keys, raising significant security concerns. The announcement comes just five days after a researcher reported the vulnerabilities, prompting immediate action from the company.
Historically, eMudhra has been a key player in the SSL/TLS certificate market, providing essential services to various organizations. However, the recent incident has forced the company to reassess its position in this sector. The compromised keys were reportedly below the recommended security threshold, making them susceptible to exploitation. As a result, both Google Chrome and Mozilla Firefox have announced plans to stop trusting the eMudhra root certificate, which will affect a substantial number of certificates issued under this authority.
In response to the situation, eMudhra has committed to replacing the affected certificates with free ones from undisclosed partners. The company has stated that its G1 RSA root certificates will continue to serve customers until all SSL/TLS certificates are either replaced or have expired. As of October 21, approximately 30,800 certificates were still linked to the compromised root, with a significant majority issued through InCommon, a service designed for the higher education sector.
The implications of this decision are far-reaching, particularly for organizations that rely on eMudhra's certificates. The company has indicated that the global SSL/TLS business accounts for about 1% of its revenue, and the complexities associated with data sovereignty and compliance have made it increasingly challenging to operate in this space. The heightened scrutiny from the incident has also contributed to the decision to exit the market.
Looking ahead, eMudhra will maintain its revocation and status services until all affected certificates are resolved. The company continues to operate in other areas, including digital signature certificates and its CertiNext platform. As the transition unfolds, organizations are advised to seek alternative certificate authorities to ensure uninterrupted service and compliance with security standards.